
LONDON — As artificial intelligence transitions from a software-dominated phenomenon into a deeply embedded hardware reality, the semiconductor industry faces a crucible moment. The race to pack billions of transistors onto advanced-node silicon to accelerate machine learning workloads has inadvertently opened the door to unprecedented security vulnerabilities.
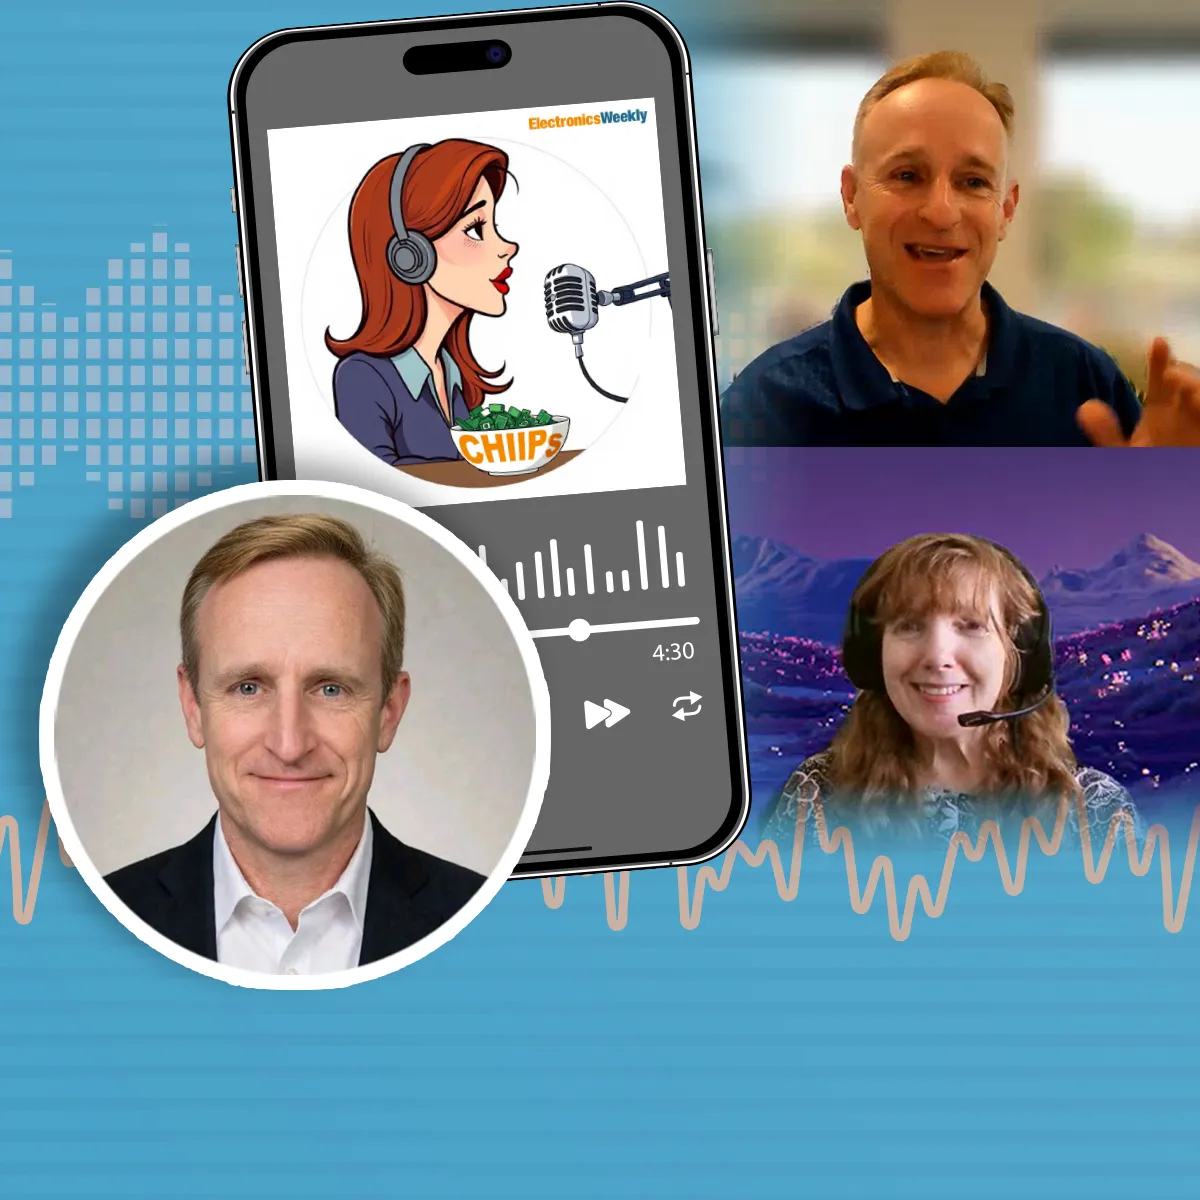
Addressing this critical juncture, the latest episode of the Electronics Weekly podcast, CHIIPS (Caroline Hayes’ Industry Insights Podcasts), tackles the complex intersection of artificial intelligence and hardware security. Hosted by veteran electronics journalist Caroline Hayes, the episode features an in-depth conversation with Michal Siwinski, Executive Vice President and Chief Product and Marketing Officer of GM Security Solutions at Arteris.
Siwinski, a seasoned executive with a deep background in semiconductor intellectual property (IP) and system-on-chip (SoC) architectures, uses the platform to dissect the necessary checks and balances required to secure AI at the silicon level. For engineers, executives, and policymakers alike, the conversation serves as both a warning and a roadmap for the future of trusted computing.
Main Facts: The Intersection of AI, Hardware, and Vulnerability
The core thesis of the latest CHIIPS episode centers on a fundamental paradigm shift in cybersecurity: software patches can no longer save compromised hardware. While the public discourse around AI security typically focuses on large language model (LLM) prompt injections, data poisoning, and algorithmic bias, Siwinski and Hayes turn the lens toward the physical layer—the silicon itself.
Key Takeaways from the Episode:
- The Paradigm Shift in Threat Models: Traditional semiconductor security focused primarily on protecting intellectual property against reverse engineering and securing cryptographic keys. Modern AI processors, however, process vast streams of dynamic, untrusted data at unprecedented speeds, creating entirely new attack surfaces.
- The Limits of Software Mitigations: In the AI era, security cannot be bolted on via software updates after a chip has been fabricated. Vulnerabilities rooted in the hardware architecture—such as side-channel leaks during neural network inference or unauthorized access to internal memory buffers—require native, hardware-enforced safeguards.
- Arteris’s Role in Ecosystem Security: As a leading provider of system IP—specifically network-on-chip (NoC) interconnects and functional safety software—Arteris sits at the dead center of modern SoC design. Siwinski outlines how configurable interconnects act as the nervous system of a chip, making them ideal control points for enforcing security policies.
- The Checks and Balances Framework: True AI hardware security demands a multi-layered approach combining pre-silicon verification, runtime monitoring, isolated execution environments (such as secure enclaves), and rigorous compliance standards across the global supply chain.
Chronology: How AI Hardware Security Became the Industry’s Paramount Concern
To understand how the semiconductor industry arrived at this critical juncture, it is necessary to trace the convergence of artificial intelligence and hardware design over the past decade.
Phase 1: The Acceleration Era (2015–2019)
In the mid-2010s, the explosion of deep learning exposed the limitations of traditional Central Processing Units (CPUs) for parallel matrix multiplication. The industry responded with a massive pivot toward specialized accelerators: Graphics Processing Units (GPUs), Tensor Processing Units (TPUs), and application-specific integrated circuits (ASICs). During this phase, performance, power efficiency, and time-to-market were the holy trinity of semiconductor design. Security was largely treated as a peripheral concern, often bolted on via auxiliary microcontrollers rather than integrated into the core architecture of the data fabric.
Phase 2: The Vulnerability Awakening (2018–2021)
High-profile hardware vulnerabilities such as Spectre and Meltdown shattered the illusion that silicon was inherently secure. These speculative execution flaws demonstrated that hardware could leak sensitive data across security boundaries even when software protocols were functioning correctly. Concurrently, as AI began moving from cloud data centers to edge devices—autonomous vehicles, medical devices, and industrial IoT—the physical attack surface expanded exponentially. A compromised AI chip at the edge no longer just meant leaked data; it meant physical danger.
Phase 3: The AI Pervasiveness and System-Level Complexity (2022–Present)
With the generative AI boom sparked by LLMs and foundation models, AI workloads became ubiquitous. Modern SoCs now integrate heterogeneous compute elements—CPUs, GPUs, neural processing units (NPUs), and specialized DSPs—all communicating over high-speed interconnects. Managing data flow, memory coherency, and security isolation across these complex multi-die and chiplet architectures became an insurmountable challenge for manual design methods.
This brings us to the present day, as highlighted by Michal Siwinski on CHIIPS. Security is no longer just about keeping bad actors out of a server rack; it is about ensuring that the foundational hardware executing AI inference and training can be implicitly trusted at every clock cycle.
Supporting Data: The Scale of the Semiconductor Security Challenge
The urgency behind Siwinski’s warnings on CHIIPS is underscored by macroeconomic trends and technical metrics defining the modern semiconductor landscape.
- Explosive Growth in SoC Complexity: Modern AI-enabled SoCs frequently integrate upwards of 50 billion to over 100 billion transistors. According to industry estimates, the design verification phase now consumes up to 70% of total engineering resources, with security verification taking an increasingly large share of that burden.
- The Financial Impact of Hardware Flaws: A software bug can be patched for pennies per user. A silicon bug requiring a hardware respin, however, can cost tens of millions of dollars in non-recurring engineering (NRE) fees and delay product launches by 6 to 12 months. In the fast-moving AI market, a six-month delay can mean total commercial obsolescence.
- The Rise of Edge AI Deployments: Market analysts project that billions of edge devices will feature dedicated AI acceleration by 2026. Each of these devices represents a potential endpoint for physical tampering, side-channel attacks, or malicious firmware injection.
- Interconnect as the Security Bottleneck: As data throughput requirements skyrocket to feed data-hungry AI models, the Network-on-Chip (NoC) acts as the primary data highway. Research indicates that failing to secure these internal pathways leaves systems vulnerable to denial-of-service (DoS) attacks where rogue intellectual property blocks critical AI processing nodes from accessing memory.
Official Responses and Industry Perspectives
The conversation between Caroline Hayes and Michal Siwinski highlights a broader philosophical shift within the semiconductor IP community. Major players are moving away from proprietary, siloed security models toward open, standards-based verification and robust architectural frameworks.
In his discussion on CHIIPS, Siwinski emphasizes that security cannot be achieved in a vacuum. It requires a collaborative ecosystem approach where EDA (Electronic Design Automation) vendors, IP providers, foundries, and system OEMs share responsibility.
"When you look at modern AI hardware design, the sheer volume of data moving across the interconnect is staggering," Siwinski notes during the podcast. "If you don’t build granular checks and balances directly into the silicon architecture from day one, you are essentially building a high-speed highway without traffic lights, guardrails, or police patrols."
Industry standards bodies are also responding. Initiatives led by organizations such as IEEE, the RISC-V International security working groups, and various automotive and industrial safety consortia are increasingly mandating strict hardware root-of-trust (RoT) implementations. Arteris, through its portfolio of configurable NoC solutions and functional safety software, has positioned itself at the forefront of this movement, providing chip architects with the tools needed to isolate security domains and monitor data transactions in real time.
Furthermore, editors and industry observers like Caroline Hayes play a vital crucial role in bridging the gap between complex engineering realities and executive decision-making. Through platforms like the CHIIPS podcast, industry leaders are given a dedicated space to unpack systemic challenges without the superficial gloss of marketing buzzwords.
Implications: What This Means for the Future of Electronics
The insights shared by Michal Siwinski on the latest episode of CHIIPS carry profound implications for various sectors across the global technology landscape.
1. For Silicon Architects and Design Engineers
Engineering teams must fundamentally alter their design flows. Security can no longer be handed off to the verification team as an afterthought before tape-out. Threat modeling must begin concurrently with architectural definition. Engineers must learn to utilize advanced Arteris NoC management tools to isolate trusted execution environments, enforce Quality of Service (QoS) guarantees to prevent starvation attacks, and implement hardware-level firewalls between disparate AI accelerators.
2. For the Automotive and Industrial Sectors
With vehicles and industrial machinery increasingly reliant on edge AI for safety-critical functions (such as Advanced Driver Assistance Systems and autonomous navigation), hardware security is synonymous with human safety. A maliciously manipulated AI model running on an unsecure NPU could misclassify obstacles with catastrophic results. Siwinski’s focus on checks and balances provides a blueprint for meeting stringent functional safety standards like ISO 26262 alongside emerging cybersecurity regulations like UN R155.
3. For Enterprise Data Centers and Cloud Providers
While data centers possess greater physical security than edge devices, they remain prime targets for sophisticated multi-tenant attacks. As cloud providers rent out heterogeneous AI clusters comprising GPUs, TPUs, and custom ASICs, ensuring absolute isolation between different customers’ workloads at the hardware level is paramount. Memory encryption, secure boot mechanisms, and runtime hardware monitoring are no longer luxury features—they are baseline market requirements.
4. For the Global Supply Chain
The semiconductor supply chain is notoriously distributed, involving design houses in the US and Europe, EDA software from specialized firms, fabrication in Asia, and packaging globally. This dispersion creates vectors for hardware Trojans and IP theft. Strengthening pre-silicon verification and establishing verifiable hardware audit trails will be essential to maintaining geopolitical and commercial trust in silicon products.
Conclusion and Next Steps
The convergence of artificial intelligence and semiconductor design represents one of the most exciting frontiers in modern technology, but it is fraught with invisible perils. As Michal Siwinski eloquently outlines on the Electronics Weekly CHIIPS podcast, navigating this terrain requires moving past naive assumptions of hardware infallibility and embracing rigorous, architectural checks and balances.
Whether you are a seasoned chip designer, an engineering manager, or an industry observer keen on the future of electronics, this episode offers indispensable insights into how the physical foundations of our digital future are being fortified.
Don’t miss the conversation! Listen to the full episode and explore past insights by visiting the official CHIIPS Podcast Page on Electronics Weekly.
Be sure to bookmark the URL and catch up on previous episodes, such as CHIIPS #39 – CHIIPs with Andrea Barrett of RS Group, as Caroline Hayes continues to chart the vital trends shaping the global electronics industry.