The industrial landscape is undergoing a tectonic shift. As manufacturers and utility operators accelerate their digital transformation, they are increasingly inviting a new class of digital worker onto the plant floor: the AI agent. However, this transition is not without peril. A typical modern plant now juggles twenty or more vendors, each eager to deploy proprietary AI agents equipped with unique access models and distinct integration requirements.
This influx of decentralized intelligence has outpaced traditional cybersecurity frameworks, creating an environment where operational technology (OT) is becoming increasingly opaque. At the Industrial AI Summit 2026, industry experts Scott Christensen of GrayMatter, Gary Tillery of Skkynet, and Ian Bramson of Black & Veatch convened to address the urgent need for governance before these agents begin executing autonomous actions on critical infrastructure.
The Governance Imperative: Managing the "Agent Explosion"
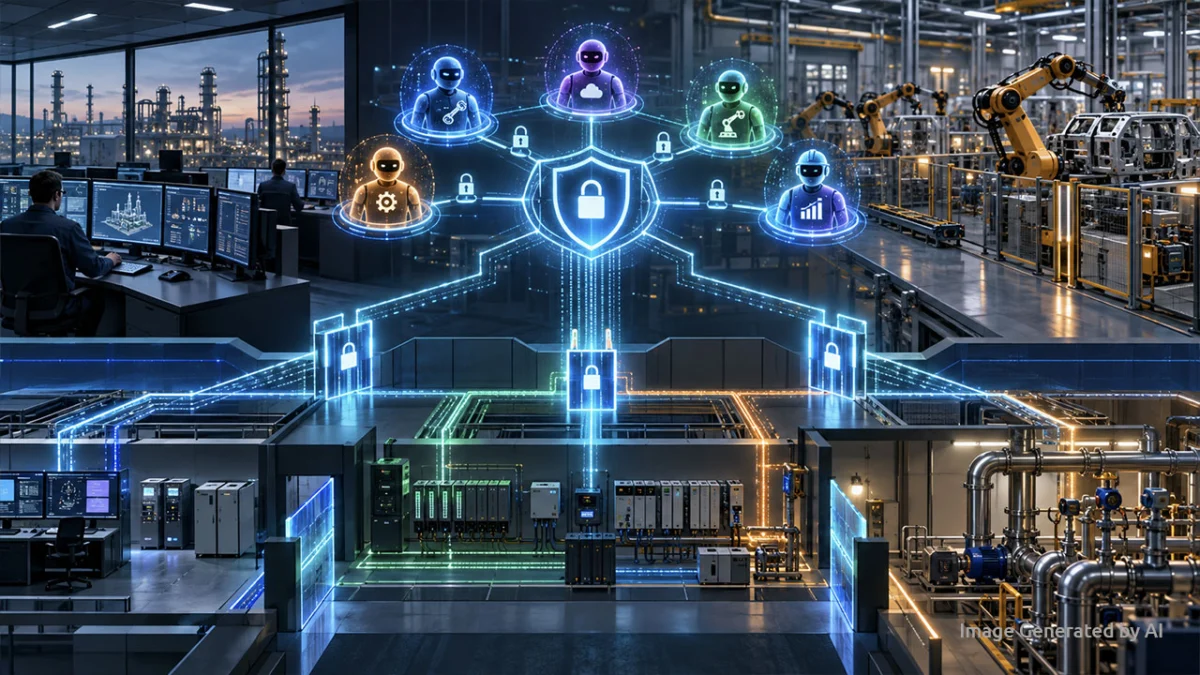
The central challenge identified by the panel is one of control. When twenty vendors independently deploy AI agents into a single OT environment, the plant faces a fragmentation of security protocols. Each agent requires its own "digital passport"—a unique set of credentials, permissions, and network access points.
"Every vendor arriving with its own version of AI brings its own access requirements, its own integration points, and its own risk profile," explained the panelists. The consensus is that plants must treat AI agents with the same rigorous scrutiny applied to human employees. This involves implementing role-based access control (RBAC), utilizing vaulted credentials, and enforcing strict network segmentation.
In the complex, interconnected world of OT, the "butterfly effect" is a significant concern. Because OT systems are deeply intertwined, a single, seemingly minor change initiated by an AI agent can trigger unforeseen consequences in downstream systems. The panelists emphasized that the era of "set it and forget it" integration is over. Governance must be active, continuous, and rooted in the principle of least privilege.
Chronology of the Crisis: From Air Gaps to Interconnected Ecosystems
To understand why the current AI integration challenge is so acute, one must look at the last two decades of industrial evolution.
- 2005–2015: The Era of the Air Gap. Industrial facilities prioritized isolation. OT networks were largely "air-gapped" from the internet, relying on physical security and local control.
- 2015–2022: The Digital Thread. Driven by the promise of Industry 4.0, plants began aggressively extracting data from the shop floor. Analytics dashboards and remote monitoring became standard, necessitating constant outbound data pathways.
- 2023–2025: The Rise of AI. Generative AI and machine learning models moved from the office to the factory. Vendors began embedding AI agents directly into programmable logic controllers (PLCs) and supervisory control and data acquisition (SCADA) systems.
- 2026 and Beyond: The Governance Vacuum. As of the Industrial AI Summit 2026, the industry is grappling with the reality that these outbound data pathways are now bidirectional, effectively creating a massive, unmanaged attack surface that necessitates an urgent pivot toward zero-trust architecture.
Supporting Data: Why Traceability is the New Currency
Data traceability is the cornerstone of effective AI governance. The panel highlighted that a generic "AI-user" login is insufficient for forensic integrity. To maintain a secure environment, an audit trail must be granular enough to answer five fundamental questions:
- Origin: Who or what initiated the AI action?
- Authorization: What permissions were active at the time of the action?
- Context: What specific data points informed the AI’s decision-making process?
- Execution: How was the change technically applied to the system?
- Outcome: What was the resulting impact on the process?
This level of detail is akin to a supply chain audit, where every raw material is tracked through the refinement process. In an OT context, an AI might recommend a set point change, but the record must provide an immutable link between that recommendation and the eventual physical execution. Without this, forensic investigation after a process upset or security breach is functionally impossible.
Official Perspectives: The "Monday Morning" Reality Check
The experts on the panel were unanimous in their belief that abstract policies are useless if they do not translate into actionable operational reality. To bridge this gap, they proposed three critical questions that plant leaders should present to their engineering and cybersecurity teams on the next working day.
1. The Resilience Question (Gary Tillery, Skkynet)
"If our connectivity went dark right now, what would still work, and who decided that?"
This question forces teams to confront the reality of their "dependency stack." It tests local resilience planning—ensuring that even if an AI agent or a cloud connection fails, the process maintains a "known-good" state.
2. The Restoration Question (Scott Christensen, GrayMatter)
"We’re very good at backing up data, but did we back up our process? Do we have our configs? Do we have our ladder logic?"
Many organizations confuse data backups (historical logs) with process backups (the logic that runs the plant). If an AI agent corrupts the logic in a controller, having a database of the last ten days of temperature readings will not restore production. This highlights the need for comprehensive disaster recovery that includes configuration files and ladder logic.
3. The Accountability Question (Ian Bramson, Black & Veatch)
"Where is our risk register for AI in OT?"
This question moves the discussion from the plant floor to the boardroom. It asks for a formal accounting of who owns the risks associated with AI, what mitigation strategies are in place, and how those risks are prioritized. A mature risk register allows for board-level oversight, ensuring that AI adoption is a business-led decision rather than a vendor-led accident.
Implications for Industrial Cybersecurity
The intersection of AI and OT necessitates a "blended" governance approach. Because no single framework currently covers the full scope of AI-driven industrial operations, experts recommend mapping core principles from the IEC 62443 standard against modern AI-specific risks.
The Five Core Principles of AI-OT Governance:
- Least Privilege: No AI agent should possess broad administrative rights. Access must be restricted to the specific, narrow function the agent was deployed to perform.
- No Autonomous Level-Zero Operation: AI agents should be prohibited from making autonomous changes at the sensor or actuator level (Purdue Model Level 0) without a "human-in-the-loop" verification step.
- Identity Persistence: Every AI agent must have its own unique, traceable identity. Shared accounts or "service account" loopholes are strictly prohibited.
- Consequence Assessment: Before any AI agent is deployed, a formal assessment of the potential physical consequences—including failure scenarios—must be completed.
- Data Flow Mapping: Every conduit between the OT environment and the outside world must be accounted for. If a data flow is not actively managed, it should be closed.
Conclusion: The Choice Between Governance and Chaos
The deployment of AI in OT is not a matter of "if," but "how." As vendors continue to push for tighter integrations, plant managers are faced with a stark choice: adopt a strategy of deliberate, policy-driven governance, or accept a state of accidental risk.
The path forward requires abandoning the "air-gap myth" and replacing it with a robust Zero Trust architecture. In this model, no agent is inherently trusted, every interaction is verified, and the impact of any failure is contained through rigorous segmentation. By asking the right questions today, leaders can ensure that the promise of AI—increased efficiency and predictive insight—does not come at the cost of operational safety and security.
As the industry moves toward 2027, the focus must shift from the novelty of AI capabilities to the maturity of AI governance. The goal is clear: an industrial ecosystem where AI acts as a reliable, transparent, and secure partner in the production process, rather than a black-box liability.