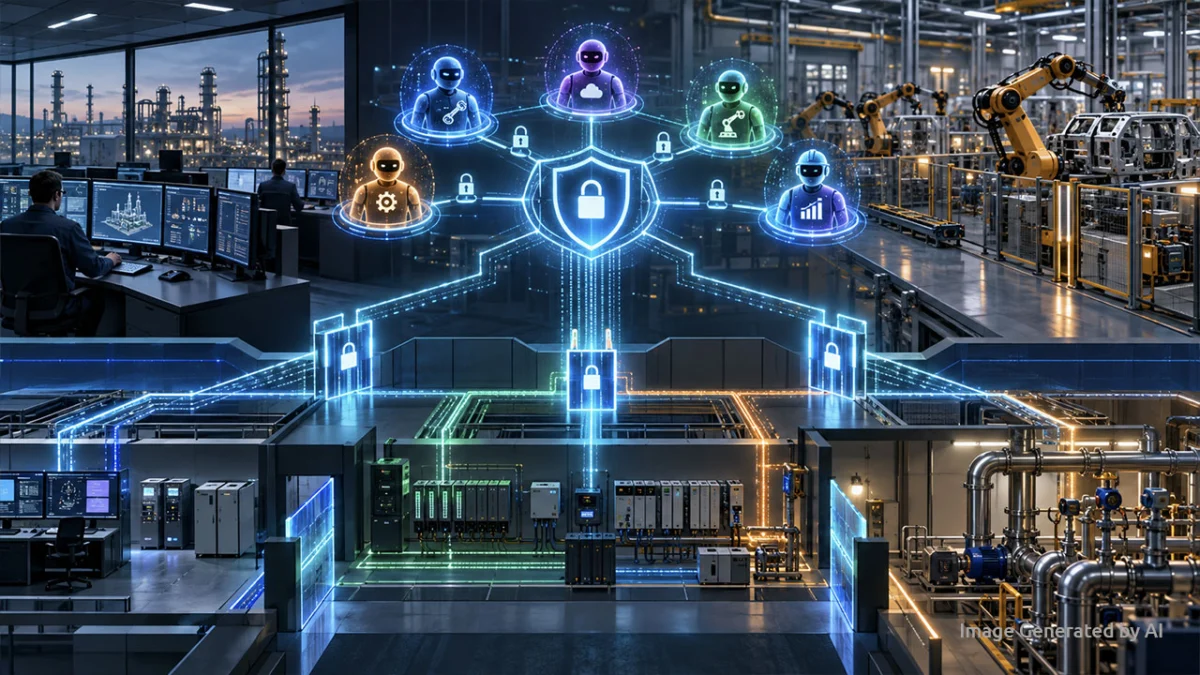
The Industrial Internet of Things (IIoT) has reached a critical inflection point. As industrial facilities increasingly adopt Artificial Intelligence (AI) to optimize production, they are encountering a new, complex challenge: "Vendor Sprawl." A single modern plant might now host 20 or more independent vendors, each deploying its own autonomous AI agent. Each agent brings unique access models, proprietary integration requirements, and distinct risk profiles.
At the Industrial AI Summit 2026, a panel of industry veterans—Scott Christensen, Cyber Practice Director at GrayMatter; Gary Tillery, CEO of Skkynet; and Ian Bramson, VP of Global Industrial Cybersecurity at Black & Veatch—convened to address the urgent need for governance. The panel argued that before any AI agent is granted the authority to take operational action in an Operational Technology (OT) environment, organizations must establish rigid, non-negotiable security controls.
Main Facts: The Reality of Autonomous Agents in OT
The integration of AI into industrial environments is no longer a theoretical exercise; it is an operational reality. However, the current deployment model is fraught with hidden dangers. When a facility grants 20 different vendors the right to deploy 20 different AI agents, it effectively invites 20 different "black boxes" into its most critical systems.
The core challenge, according to the panel, is that OT environments were never designed for the rapid, iterative deployment cycles characteristic of software-as-a-service (SaaS) AI. In traditional IT, a "move fast and break things" philosophy might result in a temporary application crash. In OT, an incorrect set-point recommendation from an unvetted AI agent could result in equipment failure, environmental catastrophe, or physical harm to personnel.
The Identity Crisis
The panel emphasized that data traceability is the foundation of AI security. An AI agent cannot be treated as a background service or a generic utility. It must be treated as a distinct user. Every agent requires its own unique credentials. Without this, forensic investigations into anomalous behavior become impossible; if a process failure occurs, incident responders must be able to pinpoint exactly which agent triggered the change, what data informed that decision, and who authorized the agent’s access level.
Chronology of the Shift: From Air-Gapped to Hyper-Connected
To understand why this is suddenly a crisis, one must look at the evolution of industrial connectivity:
- 2000–2010 (The Era of Isolation): Industrial plants relied on the "Air Gap." Operational technology was physically separated from the outside world. Security was a matter of physical access control.
- 2010–2020 (The Digitization Wave): The industry pushed to get data off the plant floor. Dashboards, predictive maintenance, and remote monitoring became standard. This era effectively ended the myth of the air gap, creating "conduits" that allowed data to flow outward to cloud analytics platforms.
- 2020–2025 (The Integration Era): These conduits became bi-directional. Systems were no longer just sending data out; they were receiving insights and automated recommendations back in.
- 2026 and Beyond (The Autonomous Agent Era): We are now in the age of the AI agent. These entities are not just providing dashboards; they are authorized to make autonomous or semi-autonomous adjustments to set points, logic, and operational parameters.
This progression has turned the "Digital Thread"—once a simple pipeline for data—into a massive attack surface. Every outbound path is now a potential pathway for an attacker or an improperly functioning AI to infiltrate the control environment.
Supporting Data: Managing the Complexity
Managing 20+ vendor agents requires a shift in philosophy. The panel proposed that governance for AI agents should mirror the gold-standard practices currently used to manage human employees:
- Role-Based Access Control (RBAC): Just as a technician is granted access only to the systems required for their job, an AI agent must be restricted to the minimum permissions necessary for its function.
- Vaulted Credentials: Hard-coded passwords or shared service accounts are unacceptable. AI agents should use dynamic, vaulted credentials that are rotated regularly.
- Network Segmentation: Even if an AI agent is "trusted," it must be contained. If an agent is compromised, segmentation ensures the damage is limited to the specific segment where it operates, preventing lateral movement across the entire facility.
- Continuous Monitoring: The "set and forget" mentality is lethal in OT. Every action taken by an AI agent must be logged, monitored, and compared against expected operational norms.
Official Perspectives: The "Monday Morning" Questions
The panelists provided actionable intelligence for leadership. The following questions serve as a litmus test for the maturity of an organization’s AI security posture:
1. Gary Tillery’s Resilience Test
"If our connectivity went dark right now, what would still work and who decided that?"
This question strikes at the heart of local resilience. If an AI agent relies on cloud-based processing to make decisions, a network outage effectively blinds the plant. Leaders must understand the "fail-safe" state of their operations. If the answer is "everything stops," the plant is overly dependent on external connectivity.
2. Scott Christensen’s Restoration Test
"We’re very good at backing up data, but did we back up our process? Do we have our configs? Do we have our ladder logic?"
Many organizations confuse data backups with operational recovery. Backing up production data is insufficient if you lose the logic that runs the machines. In the event of a ransomware attack or an AI-induced system corruption, the ability to restore the logic—the PLC configurations, the ladder logic, and the set-point parameters—is the difference between a minor disruption and a multi-week shutdown.
3. Ian Bramson’s Risk Management Test
"Where is our risk register for AI in OT?"
Risk registers are often buried in IT departments. Bramson argues that AI risks must be elevated to the board level. A well-developed risk register identifies who owns specific risks, what the mitigation strategy is, and how those risks are prioritized. If a company cannot clearly articulate its AI-related risks to the board, it has not yet established a governance framework.
Implications: Building a Sustainable Governance Framework
The panel concluded that while no single "off-the-shelf" framework currently covers the intersection of OT cybersecurity and AI, organizations should not wait for one to be written. The practical solution is a hybrid approach.
The Five Core Principles of AI Governance in OT:
- The Principle of Least Privilege: An agent should never have more power than it needs to complete its task.
- No Autonomy at Level Zero: AI agents should never be allowed to make unmonitored changes at the physical control level (Purdue Model Level 0/1). Human-in-the-loop validation is required for critical adjustments.
- Identity and Auditability: Every action by an AI agent must be logged with a unique, cryptographically verifiable identity.
- Pre-Deployment Consequence Assessment: Before an agent is deployed, a "what-if" analysis must be conducted to understand how its potential failures will affect downstream systems.
- Data Flow Analysis: Before adding an agent, map every communication conduit. Understand exactly what data is entering the plant and what commands are being sent back out.
The Zero Trust Mandate
The ultimate implication is that the "Zero Trust" model is no longer optional for industrial facilities. In a Zero Trust environment, no agent—regardless of the vendor’s reputation—is trusted by default. Every action requires justification, every data packet is inspected, and access is strictly governed.
As AI continues to proliferate, plants face a binary choice: implement deliberate, rigorous governance or accept the "accidental risk" of uncontrolled automation. The former requires significant effort, cross-departmental collaboration, and a shift in culture. The latter, as the panel warned, is a gamble that the industry can no longer afford to take.
By treating AI agents with the same scrutiny as human contractors, and by asking the difficult questions regarding resilience and recovery, plant leaders can harness the power of AI without compromising the safety and integrity of their operations. The path forward is not to stop innovation, but to govern it with the same precision that defines the industrial sector itself.